The Procurement Gap: How EU Fragmentation Invites Chinese Infrastructure Dominance
AI-generated image · US National Wire
A lack of unified risk standards is allowing state-backed vendors to embed themselves in European networks, creating strategic dependencies that are difficult to unwind.
The European Union is currently operating with a fragmented approach to technology procurement that, according to the Royal United Services Institute (RUSI), exposes member states to significant security and economic risks. The core of the problem is a lack of cohesion; while the EU has attempted to create guardrails, the resulting "hodgepodge" of policy allows individual nations to prioritize short-term cost savings or trade relations over the collective security of the bloc.
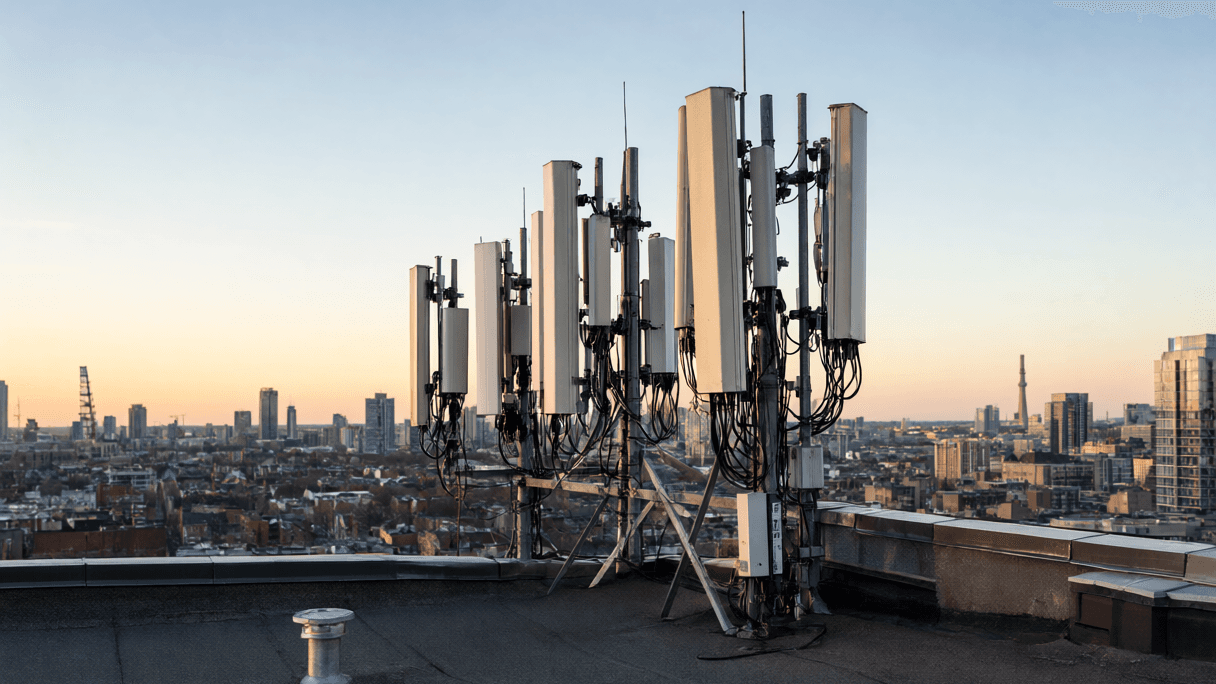
As first reported by The Register, the EU's primary mechanism for securing 5G networks—the EU Toolbox for 5G Security launched in January 2020—is entirely voluntary. This lack of enforcement is evident in the adoption rates: only 10 of the 27 member states have fully implemented the framework. This regulatory vacuum has created a backdoor for Chinese vendors, specifically Huawei and ZTE, to integrate deeply into critical infrastructure.
The disparity in how member states handle these vendors illustrates the strategic vulnerability. RUSI highlights three distinct approaches:
* **Germany:** Driven by a trade relationship with China valued at €251.8 billion ($284.4 billion) annually, Germany has historically prioritized economic ties. Consequently, Chinese suppliers made up an estimated 59 percent of Germany’s 5G RAN in 2024. While RUSI notes a slow shift under Chancellor Friedrich Merz, a material change to the 5G RAN stack is not expected soon. * **Spain:** Often favoring cost-effective options, Spain’s 5G RAN was estimated to be 32 percent Chinese-owned in 2024. The country’s approach was highlighted by a controversy last year when Huawei was awarded a contract to store judicial wiretap recordings. * **The United Kingdom:** In stark contrast, the UK is moving to completely remove Chinese technology from its telecoms network by the end of next year, aligning with U.S. security concerns.
**Opinion:** This inconsistency is more than a bureaucratic failure; it is a strategic liability. By allowing members to "wangle" their way around security descriptions, the EU is permitting the creation of "unwelcome dependencies." When one member state prioritizes the lowest bid or a trade partnership, they aren't just making a national procurement choice—they are introducing a vulnerability into the shared European infrastructure.
RUSI warns that these risks are well-founded due to the Chinese government's ability to control companies like Huawei. This includes demanding data, hosting Chinese Communist Party (CCP) representatives, and a law requiring companies to report vulnerabilities to the Chinese government within 48 hours while withholding that information from overseas counterparts. This effectively turns private security research into a state-controlled pipeline for intelligence services.
To counter this, the European Commission has proposed amendments to the Cyber Security Act (CSA). If passed, the Commission could establish a list of "untrusted vendors"—with Huawei and ZTE already indicated as candidates—that would be banned from 18 critical sectors. Any nation utilizing equipment from these designated vendors would be required to remove and replace the technology within a 36-month window. However, the effectiveness of this move depends on the EU first establishing a legal definition of a "high-risk vendor," a category that currently does not exist.