The Vendor Shield is Dead: MAS Signals Hard Line on AI Liability
AI-generated image · US National Wire
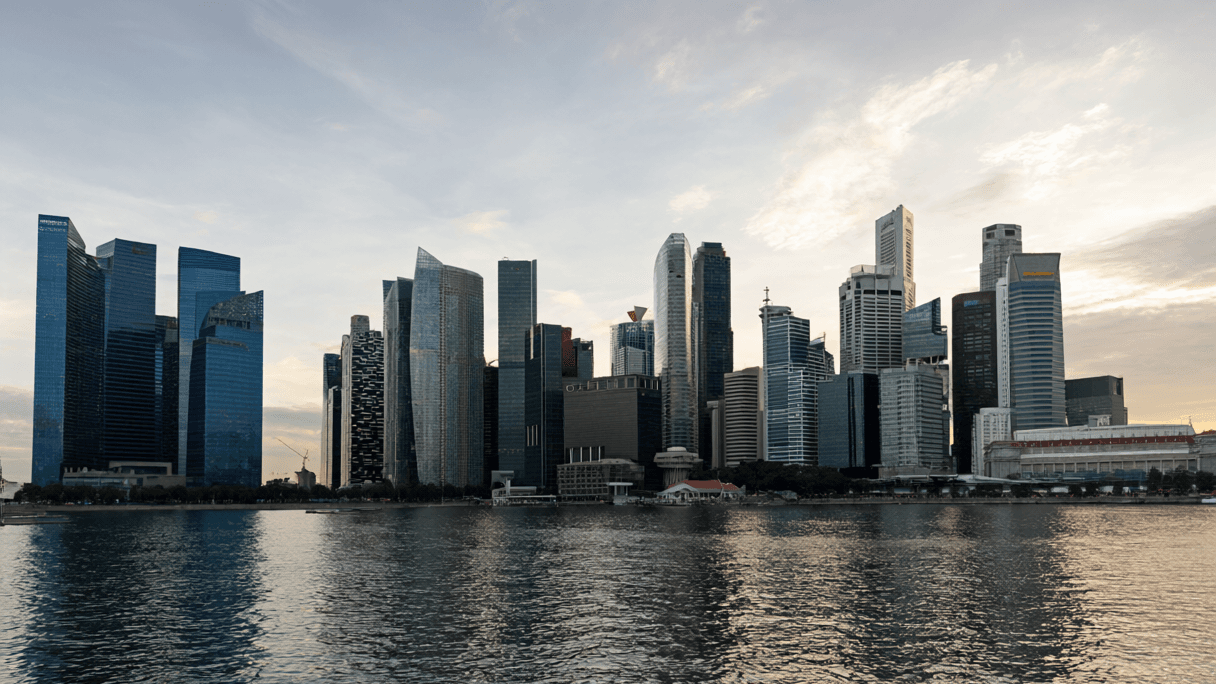
Singapore's central bank is making it clear that outsourcing AI doesn't mean outsourcing accountability, demanding independent reviews and strict oversight of third-party models.
In the world of fintech, the 'third-party vendor' excuse has long been a convenient shield for institutions when outsourced software fails. But according to new guidelines from the Monetary Authority of Singapore (MAS), that shield is officially gone.
Reporting from The Register reveals that MAS, which serves as both the central bank and the finance industry regulator for the island nation, is implementing a rigorous new framework for Artificial Intelligence Risk Management for Financial Institutions. As The Register first reported, the core message is blunt: financial institutions (FIs) are solely accountable for the AI they use to deliver services, regardless of whether that AI was developed, operated, or provided by an outside vendor.
From a market perspective, this is a critical shift in liability. MAS is signaling that FIs cannot simply point to a service-level agreement when an automated system malfunctions. Instead, the regulator expects FIs to proactively monitor third-party products to ensure stability and security. If a vendor's AI cannot be brought within the institution's risk appetite, MAS suggests the FI should consider replacing, suspending, or limiting that service.
The regulator's concern stems from the inherent volatility of these systems. As reported by The Register, MAS guidelines state that the "probabilistic nature" and complexity of AI can lead to biased behavior and greater uncertainty than simpler methods. This risk is amplified with Generative AI, which MAS views as even riskier due to potential noise in training data or scenarios the model has never encountered. The regulator further warns that "agentic AI" could amplify these risks even more.
To mitigate this, MAS is mandating a "trust but verify" architecture. Every AI use case must undergo an independent review by parties not involved in the development process before it ever hits production. This ensures that testing and evaluation controls were actually followed. Furthermore, FIs are required to conduct technology and cybersecurity reviews to ensure the production environment is secure.
MAS is also targeting the "black box" problem. The regulator requires that entities maintain an up-to-date record of every AI system employed within their business. In cases where third-party providers use AI without disclosing it, FIs are tasked with finding ways to manage the risks associated with these "unknowable" AI contributions.
Finally, the regulator is demanding a safety net. For high-risk applications, FIs must develop contingency plans and fallback options—including manual processes or alternative systems—to ensure business continuity if the AI exhibits unexpected behavior or fails entirely.
These guidelines are set to come into force on October 7, 2027. For the banks and fintechs operating in one of the world's premier finance hubs, the mandate is clear: you own the risk, no matter who wrote the code.