The Perimeter is a Fantasy: Federal Identity Failures Leave Millions Exposed
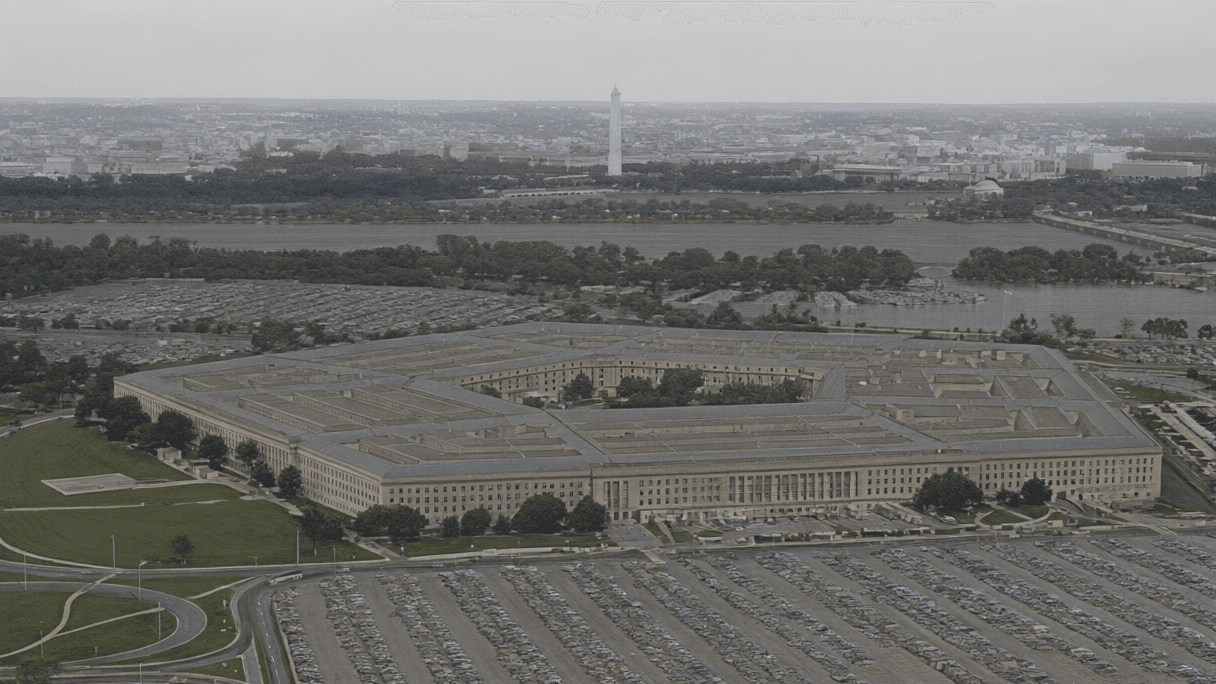
AI-generated image · US National Wire
Recent breaches at the Pentagon and FBI prove that sensitive government personnel data is essentially public, creating a goldmine for foreign intelligence.
*(Opinion)*
For years, the federal government has operated under the delusion of a secure perimeter. But the recent collapse of identity and access management across our most sensitive agencies proves that this perimeter is a fantasy. When the very systems designed to track our defenders are compromised, we aren't just dealing with isolated glitches; we are witnessing a systemic failure that renders our most sensitive data effectively public.
As Ars Technica first reported, the Pentagon is currently notifying over 2 million current and former military members that their personnel records were stolen. This wasn't a quick smash-and-grab. The breach involved a monthslong compromise of a network operated by the Defense Manpower Data Center, which manages more than 60 million records for contractors, civilians, retirees, veterans, military personnel, and their families.
According to Ars Technica, the stolen data included names, addresses, sex, race, Social Security numbers, and occupational specialties. From a threat-modeling perspective, the theft of occupational specialties is the most alarming detail. This data allows foreign adversaries to surgically identify high-value military personnel, turning a database into a target list for intelligence agencies.
This isn't an isolated incident. Ars Technica notes that this follows a breach last month where the ransomware group ShinyHunters claimed to have infiltrated FBI systems. As reported by Reuters, the stolen records of thousands of current or former FBI employees included job titles specifically linked to investigations involving Russia or China. While ShinyHunters claims it has no intention of releasing the data, such promises from a criminal organization are meaningless. Even if the criminals hold the data, they are rarely the only ones with access; nation-state hackers are far more capable of bypassing the defenses of criminal groups.
FBI Cyber Division Assistant Director Brett Leatherman has called for ShinyHunters members to surrender, noting that the FBI is continuing to learn more about the group following the arrest of one member by Dutch police. But law enforcement pressure does nothing to recover the data already exfiltrated.
We have seen this movie before. Ars Technica compares these recent failures to the 2015 hack of the US Office of Personnel Management, where Chinese state hackers stole 22.1 million records, including fingerprint scans. The fact that we are repeating these mistakes in 2026 suggests a fundamental refusal to accept that identity is the new perimeter.
The Pentagon has yet to explain how the Defense Manpower Data Center was breached or if ransom demands were made. While officials claim the stolen data hasn't been misused, they have provided no explanation for how they reached that conclusion. In the world of cybersecurity, silence isn't security—it's a vulnerability. If you can't explain how you're protecting the data, you aren't protecting it.