The 'Good Faith' Dragnet: Met Police's Governance Collapse
AI-generated image · US National Wire
A reprimand from the ICO reveals how London's Metropolitan Police bypassed privacy laws to use a retail crime platform, signaling a systemic failure of technical oversight.
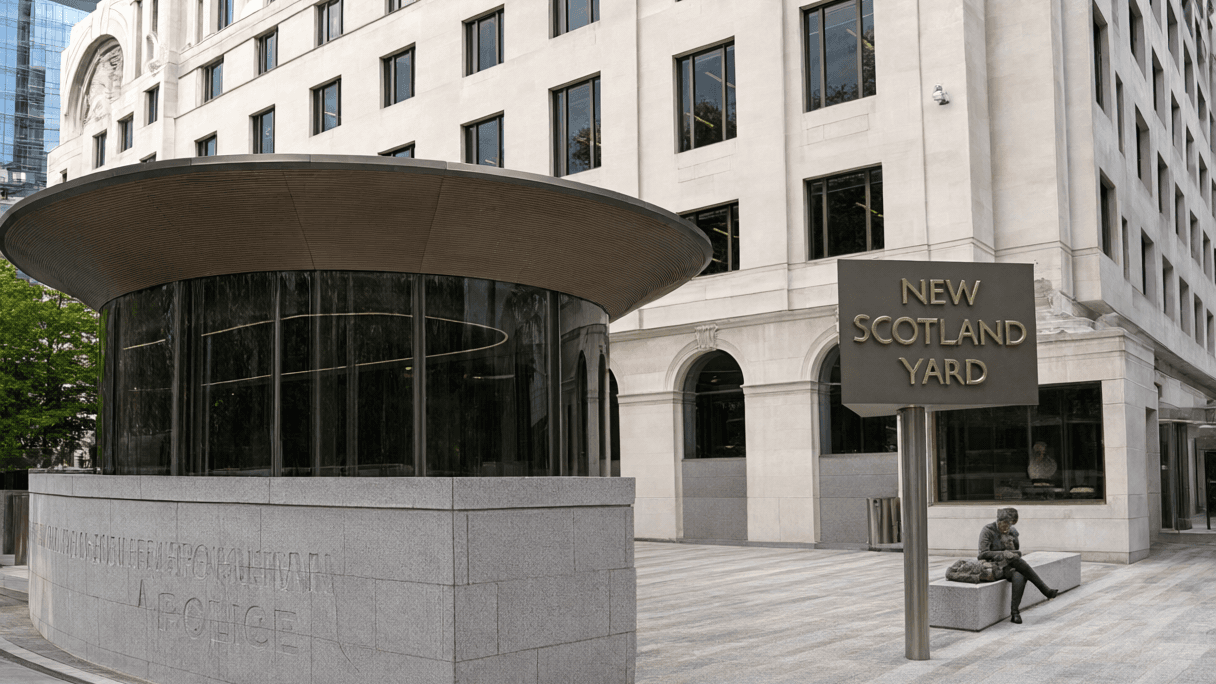
In the world of cybersecurity, 'good faith' is not a substitute for a firewall. As reported by The Register, the Information Commissioner's Office (ICO) has reprimanded London's Metropolitan Police Service (MPS) for allowing officers to operate a retail crime platform, Auror, without formal procurement, data protection checks, or a data protection impact assessment (DPIA).
This wasn't a minor lapse; it was a systemic failure. Between March 2023 and September 2024, officers registered roughly 500 free accounts on Auror, a platform used by retailers like Tesco, Boots, Greggs, and M&S. The result? The unlawful upload of personal data for 179 people, including three children. For 128 individuals, names were uploaded; 49 had dates of birth added, and two had their home addresses exposed.
**Opinion:** This is the 'move fast and break things' mentality applied to state surveillance. When law enforcement prioritizes 'positive outcomes' over legal safeguards, they turn public safety tools into unchecked dragnets. The MPS's reliance on 'soft controls'—training and reminders—over technical blocks is a dereliction of duty. If your web controls don't trigger an alert while officers use unapproved software for 18 months, your security posture is nonexistent.
The ICO noted this is a repeat failure, citing a 2021 incident involving Clearview AI. Despite the breach, the MPS is already rolling the tech back out in 14 London boroughs, claiming it has 'quadrupled positive outcomes' for shoplifting. While the MPS claims to have now completed necessary legal and security checks, the ICO's enforcement action highlights a persistent inability to prevent these incidents. As David Doodson, head of investigations at the ICO, stated, technology must be used lawfully and transparently from the outset—not retroactively patched after the privacy damage is done.